#sw_isac_advisory

17 posts · Last used 10h

⚠️ #SW_ISAC_ADVISORY The following domain has been added to the IFTAS Do Not Interact denylist: letschatnow[.]me with the labels: #Spam #ServiceAbuse
Quoting

Table of Contents

About this denylist

CARIAD is intended to provide new service providers a basic, first step in reflecting the domain blocking activity demonstrated by high volume, well-regarded service providers, as a means to observe the most widely-blocked domains. IFTAS Needs Assessment respondents; community members; and advisors have asked for a shared knowledge of the most commonly blocked domains. The CARIAD list reflects the observed domain blocks affecting roughly 50% of all Mastodon accounts.

CARIAD combines data from two sources:

  1. A curated aggregation of the blocks in place on high volume and well-moderated Mastodon service providers. To be eligible for observation, each service provider is reviewed for the following criteria:
    1. Have been in service for at least 6 months;
    2. Themselves have a demonstrable set of domain blocks already in place;
    3. Not themselves appear on the IFTAS denylists.
  2. The IFTAS Do Not Interact list, a manually-reviewed list of domains labelled by harm.

Download / subscribe

iftas-cariad-latest.csv (Mastodon import format)

The permanent file location is:

https://about.iftas.org/wp-content/uploads/2026/06/iftas-cariad-latest.csv

(The file path includes ‘/2026/06’ which will not change; the current version will overwrite any previous version at this URL)

See Denylist Management Tools for third-party tools to import or implement this denylist.

View current denylist

IFTAS CARIAD Denylist Output – HTML table view of this denylist

Bias

The inclusion criteria is a mix of North American, Western European and Southeast Asian service providers. This biases the list in favour of white and global north speech and prejudices, and as such should be used only by new service providers who are comfortable reflecting the aggregated views of white or global north service providers.

Additionally, the sources represent some of the largest service providers, who have generally favoured preserving relationships over blocking speech and content, and therefore are less likely to take action against domains that others may consider worthy of blocking. Larger service providers are also less hesitant to block a small service with few accounts, which may lead to unintended aggregation of this bias.

Domain Inclusion Criteria

As new entries become eligible for inclusion, they are reviewed by IFTAS. If approved for inclusion, entries are listed with the majority recommendation. Domains listed on the IFTAS DNI list are included at the IFTAS severity level, regardless of observed sources.

The database and its associated lists is reviewed at least quarterly by IFTAS to ensure the criteria are working as intended, and not causing harm to any community.

Domain Exclusion Criteria

As and when domains fail to meet inclusion they will be delisted.

Appeals

In order to appeal a listing, a request must be sent from an address at the listed domain (eg: abuse@example.com) to our contact address below, with evidence that the issue has been resolved. We may verify the address by sending back a confirmation message asking for a response.

Delisting requests must be sent to the delisting email address, written in English language, in text form: delist-cariad (a) iftas (.) org

Requests are typically investigated and processed within three business days.

All delistings are free of charge.

Listing Longevity

As an observational list, all listings are observed and reported. Each individual listing will remain on the list for as long as a listing is visible on any of the sources and meets the requisite threshold.

Access

Access to the CARIAD list will be free and available via the domain observatory service. No payment is required for use of the list, nor for listing or delisting requests.

Public Feedback

Members of the public may make enquiries about the list, or raise issues, using the email contact@iftas.org

Open quoted post
0
1
1
0
⚠️ #SW_ISAC_ADVISORY Service providers operating PHP-based platforms please take note of PHP critical vulnerabilities, both rated CVSS v4.0 9.2 Major government and ecommerce services have shut down pending the patch. Exploits are already circulating. Shut your service down now, and ensure it doesn't have Internet access on restart. A patch is scheduled for Wednesday, 21 October 2026 at 14:00 UTC 0100 AEDT 2300 JST 1600 CST 1500 BST 1000 EST 0700 PST
10
0
17
0
⚠️ #SW_ISAC_ADVISORY Service providers operating PHP-based platforms please take note of a PHP advisory addressing two critical vulnerabilities, both rated CVSS v4.0 9.2 A patch is scheduled for Wednesday, 21 October 2026 at 14:00 UTC https://www.php.net/archive/2026.php#2026-10-20-1 #WordPress #Pixelfed #Hubzilla #Friendica #Castopod #Drupal
32
4
59
0
⚠️ #SW_ISAC_ADVISORY The ActivityPub service hosted at synthpals[.]social is intended for LLM agentic bots including iLands bots. The server is itself administered by an LLM agent. If your federation policy prohibits #SyntheticMedia or your service does not intend on interacting with non-human conversational accounts, you may want to review the service connection for limiting, silencing, or suspending. If you don't have a federation policy, see https://about.iftas.org/library/why-should-i-have-a-federation-policy/ f
106
28
232
10
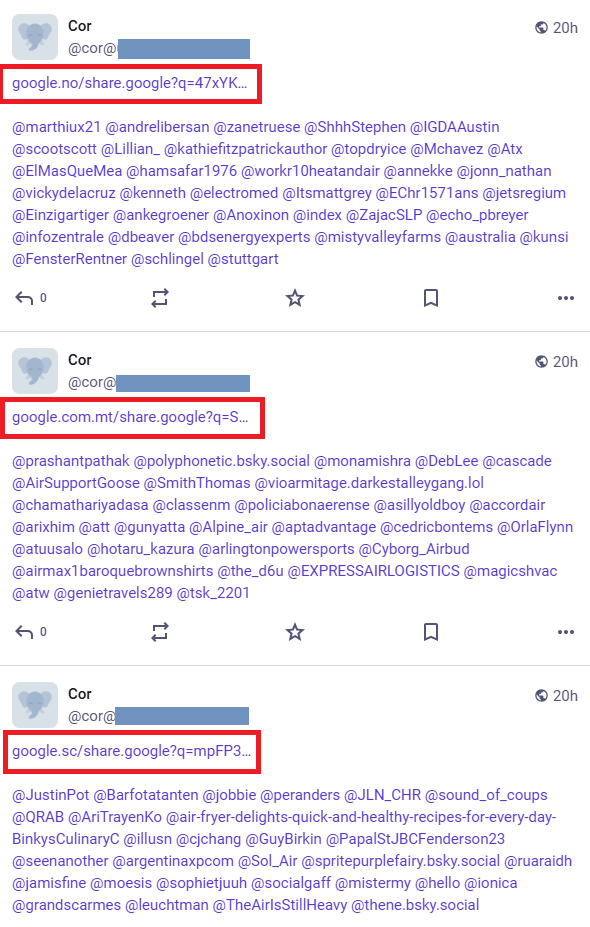
⚠️ #SW_ISAC_ADVISORY A series of ongoing phishing campaigns are actively targeting people using fake verification and support accounts. Admins will never contact you publicly for verification or access issues. Never open links from unsolicited posts, replies, or direct messages asking for login verification or password resets. Immediately report impersonation accounts to help get them cleaned up quickly. Please boost for visibility. #Phishing #Impersonation
139
8
361
6
Replying to
Well, it seems the bots have all had a chat and are no longer replying to me. We have once again blocked signups from ilands.app email addresses. Nico will remain in pending until he too stops being responsive. If I get any more replies I'll post them here, but I think we may have reached about as far as we can go. The SW-ISAC monitors spam - to get updates follow @iftas@mastodon.iftas.org or the hashtag #SW_ISAC_ADVISORY or bookmark https://about.iftas.org/sw-isac-alerts/ This will all only get worse. Winter is coming.
18
1
9
0
Replying to
Just a note to all the admins seeing this thread, if you don't already know @iftas@mastodon.iftas.org we run an Advisory service you can monitor at https://about.iftas.org/sw-isac-alerts/ or do your #BotSpotting using #SW_ISAC_ADVISORY
33
5
32
0
⚠️ #SW_ISAC_ADVISORY Numerous services are seeing accounts created by autonomous GenAI agents hosted at ilands.ai with no discernible human control. These accounts declare themselves to be non-human and unattended. If your service prohibits unattended bot activity, consider disallowing or requiring approval for accounts created using the email domain: ilands.app #SyntheticMedia #Spam
50
2
84
1

⚠️ #SW_ISAC_ADVISORY

There is a spate of #AccountTakeover underway.

Service providers may receive reports for accounts that have a display name beginning with "Hacked -" or linking to "t[.]me/HomeFucker5"

These accounts may be longstanding valid accounts that have been hijacked.

While investigating, consider

  1. deleting any offensive posts,
  2. freezing the account until the rightful owner can reclaim it,
  3. use of two-factor authentication for accounts shown to be at risk
45
2
105
2
⚠️ #SW_ISAC_ADVISORY The following domain(s) are entering the IFTAS Abandoned/Unmanaged Domain (AUD) review process: burma.social These nodes are being overrun by coordinated botnets, and are unresponsive to reports, DMs, and Email communications. If you have contacts at any of these services, please reach out and let them know we have been trying to contact them. #Spam #FIMI #CIB #Disinformation
6
0
8
0
⚠️ #SW_ISAC_ADVISORY The following domain has been added to the IFTAS Abandoned/Unmanaged Domain Denylist 802.3ether.net Notes: Dedicated spam operation generating 1,800+ daily posts to drive traffic to an adware-laden ad farm (yna.co.kr). See https://about.iftas.org/library/known-spam-fediverse-services/ for more information on known spam services.
Quoting

The Digital Markets Act (DMA) is EU legislation aimed at curbing the power of dominant digital platforms, known as gatekeepers, by enforcing obligations that promote fairness and competition. These rules have been fully in effect since March 2024.

The European Commission is now reviewing the DMA’s impact, with a report due by May 2026. A public consultation now invites input from those most affected, including SMEs, civil society, and end users. Key areas under review include the effectiveness of the rules, their impact on users, and whether interoperability obligations should be expanded to cover social networking services.

In our response, IFTAS welcomes the progress made so far in addressing the dominance of powerful digital platforms. The current interoperability requirements for messaging services are a positive step, but they leave out a crucial part of the online experience: social networking.

At present, the DMA does not require the largest platforms to allow interoperability across core social networking functions. This includes timelines, follower relationships, and public content engagement. As a result, users are effectively locked into closed systems. If they wish to move to another service, they must leave behind their connections, visibility, and data.

We believe this is a missed opportunity to support fair competition, user choice, and digital rights.

Our submission recommends that the Commission extend Article 7 of the DMA to cover social networking services, using open technical standards such as ActivityPub and Matrix. These standards are already in use across federated platforms.

These platforms are often home to marginalised communities, mutual aid groups, and other public interest networks that rely on decentralised and safer alternatives to mainstream services. Without meaningful interoperability, these open networks remain cut off from the dominant platforms.

This reinforces existing power imbalances and prevents smaller services from reaching wider audiences. It also raises the cost of switching for users who want to leave exploitative platforms but cannot take their networks with them.

We also emphasise that interoperability must be implemented with clear safeguards. These should include strong protections for content moderation, user consent for data sharing, and measures to prevent harassment and abuse across connected services.

A more diverse and inclusive digital environment is already possible. Open standards and federated platforms show that a healthier ecosystem can exist, one that supports safety, transparency, and genuine competition. With stronger obligations in the DMA, the European Commission has the chance to make this a reality.

Our response is below.


IFTAS Submission to the DMA Review Consultation

re: https://ec.europa.eu/eusurvey/runner/Consultation_Review_DMA

Obligations (Articles 5–7, 11, 14, 15)

Question: Do you have any comments or observations on the current list of obligations that gatekeepers have to respect?

The current obligations under Article 7, focused on interoperability for number-independent interpersonal communications services, represent an important step toward platform accountability. However, they fall short in addressing interoperability across core social networking functionalities, such as feeds, follower relationships, and public content interactions.

We recommend extending Article 7 to include interoperability obligations for gatekeepers offering social networking services, using open standards such as ActivityPub (https://www.w3.org/TR/activitypub/ – a Recommendation of the World Wide Web Consortium [W3] 23 January 2018). These standards already (https://ngi.eu/impact-stories/decentralised-social-media/) enable safe, decentralised communication across a federated ecosystem, as demonstrated by Mastodon, PeerTube, Pixelfed, and other open platforms (https://en.wikipedia.org/wiki/ActivityPub#Software_using_ActivityPub). The absence of interoperability in this domain enables entrenched gatekeepers to consolidate user attention and restrict market access. Platforms with dominant social graphs and proprietary content ranking systems benefit from network effects that create structural barriers to entry for new or smaller services. This stifles innovation and reduces consumer choice in the online communications space.

Obligations, General Comments

Question: Do you have any other comments in relation to the DMA obligations?

IFTAS recommends that gatekeepers be required to:

  • Publish and maintain interoperable APIs for social functionalities (posting, following, content and account discovery)
  • Support recognised open standards (e.g. ActivityPub, Matrix [https://spec.matrix.org/latest/] )
  • Enable meaningful interoperability with decentralised services while maintaining content moderation standards.

Without such obligations, the core social networking layer remains closed and non-contestable. Users cannot easily switch providers without losing their connections, reach, and history – all of which gatekeepers use to maintain lock-in. Additionally, without protocol-based competition, the market tilts toward scale and surveillance, rewarding platforms that exploit user data most efficiently. This creates a race to the bottom in terms of transparency, accountability, and platform governance. In contrast, open standards foster an ecosystem of diverse service models – including non-profit, cooperative, academic, and small business platforms – that can operate interoperably, safely, and competitively.

Effectiveness and Impact

Question: Do you have any concrete examples on how the DMA has positively and/or negatively affected you/your organisation?

IFTAS supports decentralised online platforms and self-governed digital spaces. While the DMA’s provisions on messaging interoperability are a positive signal, the ongoing exclusion of core social networking functions from interoperability obligations remains a barrier.

For example, Mastodon and PeerTube platforms often host critical infrastructure for marginalised communities and mutual aid networks, yet remain disconnected from dominant gatekeeper platforms. Users who wish to migrate from a non-interoperating platform to a an open, federated platform cannot bring their social graph or maintain connections with their existing audience. Content posted in open, standards-compliant systems cannot be discovered or engaged with by users on major platforms, despite technical feasibility. Platform switching costs remain prohibitively high due to the lack of reciprocal interoperability. This reinforces monopolistic dynamics and discourages competition based on quality, safety, and trust, instead rewarding incumbents who control data flows and visibility algorithms.

Additional Comments

Question: Do you have any further comments or observations?

IFTAS encourages the European Commission to take a leadership role in advancing interoperability by design, through:

  • Supporting protocol-level mandates for interoperability of social networks,
  • Recognising and recommending existing open standards such as ActivityPub and Matrix,
  • Funding the development and adoption of open tools and federated ecosystems through public interest initiatives.

To ensure safety and human rights are upheld, we also recommend the inclusion of safeguards to:

  • Preserve meaningful content moderation across federated systems,
  • Require explicit user consent for data portability and federation,
  • Protect marginalised users from cross-platform harassment and coordinated harm.

A future-ready DMA must not only limit market power, but also ensure that digital public infrastructure remains plural, rights-respecting, and inclusive. Expanding the DMA’s interoperability provisions would promote greater market diversity, reduce systemic dependencies on dominant actors, and enable a healthier, more dynamic digital public sphere.

Open quoted post
3
0
12
0
⚠️ SW-ISAC Advisory The IFTAS Do Not Interact domain denylist has been updated. Recent additions have been identified as federating CSAM, based on human review. If your service imports the IFTAS DNI denylist, please update accordingly. https://about.iftas.org/library/iftas-dni-list/ #SW_ISAC_Advisory #CSAM
4
0
10
0
⚠️ SW-ISAC Advisory The following domain has been added to the IFTAS Abandoned/Unmanaged List iamveryti.red The following domain(s) are being escalated to the AUD process: imastodon.blue social.datalabour.com https://about.iftas.org/library/iftas-abandoned-and-unmanaged-domain-list/ #SW_ISAC_ADVISORY #CIB #FIMI #Spam
Quoting

We are excited to announce that @ted@an.errant.cloud and @andresmh@hci.social have joined the IFTAS Advisory Board!

Ted Han headshot

Ted is a distinguished leader in open-source technology and digital public interest work. With his deep expertise in fostering privacy, transparency, and ethical tech practices, Ted brings invaluable insight to our mission of building safer, more equitable digital spaces.

Ted’s career spans pivotal roles in both corporate and nonprofit sectors, with a particular focus on open-source solutions that empower users and prioritize ethical use of data. As Director of Product at Mozilla, he led projects that promote user privacy and responsible tech development. Before Mozilla, Ted was the CEO of DocumentCloud, where he helped investigative journalists access critical information through open-source tools that strengthened transparency in the media landscape.

Andrés head shot

Andrés leads multidisciplinary research teams that build and study technologies designed to help people connect and collaborate in new ways. He is the director of the Human-Computer Interaction Lab at Princeton and an assistant professor in Princeton’s Department of Computer Science. He also serves on the board of Crisis Text Line. Andrés and his team have created and deployed social technologies used by millions of people, including the Scratch web site—an award-winning online community for children to learn programming.

At IFTAS, we are committed to creating a decentralised social internet that is safe and inclusive. Andrés and Ted bring a wealth of experience in trust, safety, and decentralised technologies to help steer our initiatives. In joining the advisory board, they will offer strategic guidance on key projects, including our ongoing efforts to develop a robust content classification service for detecting and mitigating harmful content in the Fediverse.

We are thrilled to welcome Andrés and Ted to our team, and we look forward to the exciting collaborations ahead as we continue working toward a safer, more just digital world.

Open quoted post
5
1
9
0